NetSuite Systems Integration
NetSuite Integration Services
Connect NetSuite with CRM, ecommerce, warehouse and reporting applications through a defined business workflow. Macrofix can scope interface design, field mapping, access, exception recovery and reconciliation. Confirm available records and account constraints before choosing a connector or custom integration.
Discuss Your NetSuite Integration
Connect Workflows Without Losing Data Ownership
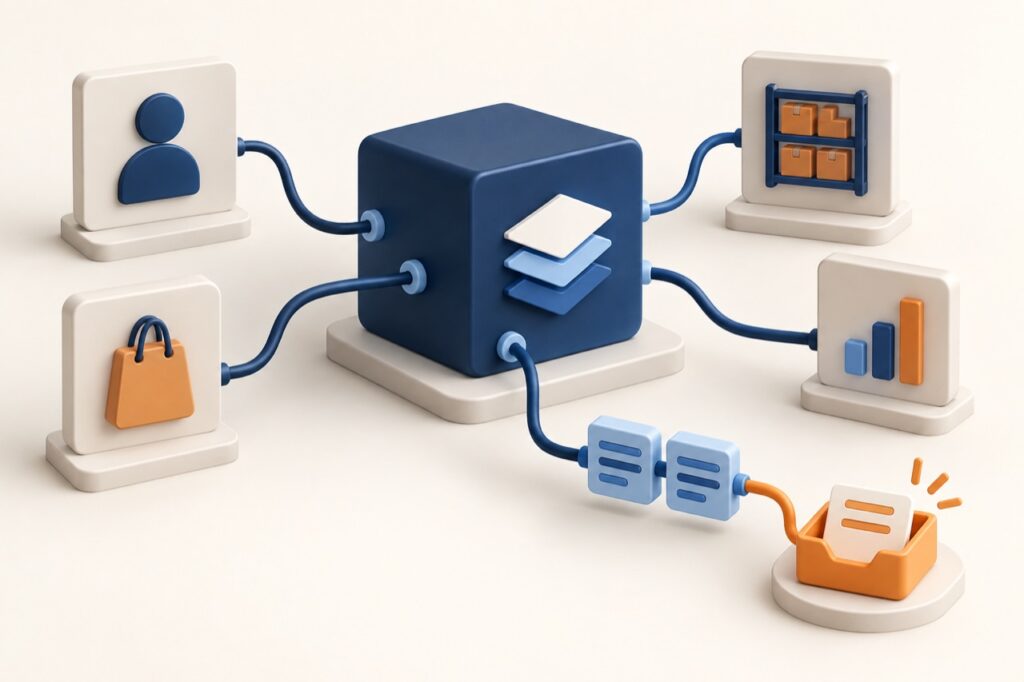
An ecommerce order, shipment update or customer change can pass through several applications. A connector can move a record without proving that the receiving system accepted the right business outcome. Integration design needs clear ownership, identifiers, validation and recovery rules.
This service covers continuing data exchange between systems. For a new ERP rollout, explore NetSuite implementation services. The NetSuite services hub covers the wider platform roadmap.
NetSuite Integration Workstreams
Select a priority process and identify the NetSuite records and external objects involved. Assess APIs, account features, permissions and operational dependencies before development. The workstreams below describe a proposed project scope, not universal connector compatibility or an assumption that every record supports every operation.
Process Scope & Interface Feasibility
Map the complete process from the initiating event to downstream acceptance. Inventory source and target systems, data owners, transaction volumes and timing needs. Identify where information is authoritative and where users handle business exceptions today.
Confirm the operations each endpoint supports and the account configuration they depend on. Separate a recurring synchronization requirement from one-time data migration, reporting extraction or a business-process redesign. Each has different acceptance and operating needs.
- Business event and complete process map
- Selected records and supported operations
- Account features and supplier dependencies
- Source and target data owners
SuiteTalk, Connectors & Integration Design
SuiteTalk REST web services provide a NetSuite integration channel. Macrofix can assess supported records, authentication, permissions and account features against the intended process, alongside approved connectors or middleware.
Compare available integration approaches before custom development. Document request and response contracts, environments, version dependencies and deployment steps. Existing SOAP integrations need a current lifecycle and transition review against Oracle’s SOAP governance guidance, not an assumption of indefinite endpoint support.
- Interface contract and synthetic payloads
- Field mappings and identifier strategy
- Authentication, permissions and secret handling
- Version, connector and capacity constraints
Field Mapping & Transaction Ownership
Define object identifiers, external references, field mappings, status translations and validation rules. Record how customers, items, orders, invoices, fulfillment or other selected objects relate across the two systems. Owners approve business mappings and exception decisions.
Specify which system may create or update each field, how changes are detected and how deletions or corrections are handled where applicable. Plan pagination and incremental extraction against actual API behavior. Use synthetic payloads in shared specifications.
- Retry and duplicate safeguards
- Business rejection and recovery routes
- Source-to-target reconciliation
- Test evidence and operational handover
Retries, Exceptions & Reconciliation
Design timeouts, backoff, retry limits and duplicate safeguards before the first live transaction. Failed validation, unavailable targets and expired credentials need distinct handling. A replay should not create a duplicate order or financial transaction.
Reconcile source and target outcomes using agreed identifiers and totals, with an exception register and responsible owner. Measure delivery timing under representative conditions. Do not treat a successful request or an empty error log alone as proof that all intended records arrived.
Testing, Release & Operating Handover
Test the complete workflow with accepted, rejected, delayed and replayed records. Include access boundaries, realistic volumes and downstream business checks. Capture results and open risks against the interface contract before production approval.
Release through the agreed environments and hand over mappings, diagnostics, recovery instructions and escalation ownership. Continuing monitoring and incident response require a defined support arrangement. A one-time integration project is not unlimited maintenance or development.
A NetSuite Interface Contract with Clear Owners
The interface contract records the business event, selected records, source and target authority, mappings and acceptance behavior. Include account and supplier dependencies, secure access arrangements, validation failures and replay rules.
Maintain traceability from a business requirement to a test and operating instruction. A readable contract lets business users, administrators and external suppliers understand their responsibilities when the connection changes or fails.
- Process scope and business acceptance owner
- NetSuite and external object definitions
- Field authority, mappings and validation
- Account access and capacity dependencies
- Failure, replay and reconciliation rules
- Release stages and support responsibilities
Account Permissions, Governance & Supplier Boundaries
Review account permissions, integration identities and secret storage with your security owners. Apply access only to the approved operations and environments, and avoid credentials or sensitive payloads in ordinary logs. Supplier terms and customer approvals remain part of the design.
Oracle documents concurrency governance across web services and RESTlet requests. We assess the account’s available capacity and competing integrations before setting throughput expectations. Subscriptions, vendor limits and external-system behavior can affect the result; no unlimited capacity or guaranteed realtime delivery is implied.
- Review account permissions and secure identities
- Confirm capacity and competing integration use
- Verify vendor and connector commercial terms
- Mask diagnostic data and retain approved evidence
From Connection Assessment to Accepted Workflow
Begin with process discovery and interface feasibility. Approve the contract, mappings, access and recovery design, then build and test in controlled environments. Review business outcomes and operating readiness before release.
Additional flows can be phased after the first workflow is accepted. Reassess capacity, object ownership and dependencies as scope grows rather than assume the original design handles every future application.
- Discover the workflow and assess interfaces
- Approve mapping, access and recovery design
- Build and test in selected environments
- Reconcile outcomes and review readiness
- Release with runbooks and named owners
Evidence for Integration Acceptance
Acceptance checks whether the intended process works and can be operated safely. Review successful and rejected transactions, duplicate controls, outage recovery and reconciliation. Record measured timing and capacity limits rather than infer performance from a small demonstration.
Confirm that alerts and runbooks reach the responsible owners. Capture unresolved risks, supplier dependencies and explicit business sign-off. Production financial or personal records require approved handling; they are not uncontrolled test fixtures.
- Accepted and rejected workflow test evidence
- Timeout, replay and duplicate scenarios
- Reconciled source and target outcomes
- Access and representative-capacity checks
- Operational handover and risk sign-off
NetSuite Integration FAQs
We can assess CRM, ecommerce, warehouse, reporting and other business applications against available interfaces and the required process. Supported records, account features, permissions and supplier terms need verification. We do not promise that every product or connector covers every operation.
The choice depends on available record coverage, mappings, recovery behavior, operations and commercial terms. We evaluate approved connectors and middleware before proposing custom development. SuiteTalk REST can be an option when its supported operations fit the requirement.
Review its endpoint, dependencies and transition requirements against current Oracle lifecycle guidance. We can scope an assessment and migration plan where needed. This page does not imply that legacy SOAP endpoints remain supported indefinitely or that every flow can be converted without redesign.
The design specifies identifiers, validation, bounded retries, duplicate safeguards and reconciliation appropriate to the process. Exceptions need an owner and an approved recovery path. Testing includes timeouts and replay; request success alone is not proof of a completed business transaction.
Timing depends on source events, APIs, concurrency, middleware, network conditions and target processing. We agree and test timing requirements in the actual environment. Guaranteed realtime delivery or unlimited throughput is not an assumption of this service page.
The project defines acceptance, documentation and operational handover. Continuing monitoring, incident response, connector upgrades and new development require an explicit support or project scope. Use the public enquiry only for non-sensitive requirements, not credentials or production records.
Scope Your NetSuite Integration Project
Tell us the applications you need to connect, the NetSuite records involved and the process you want to complete. Macrofix can propose a feasibility assessment and integration scope. Return to the NetSuite services hub for related projects. Do not include tokens, API keys, passwords or confidential business records in your public enquiry.